
· Updated
By DMARCdrift
What Is DMARC Monitoring? The Visibility Layer Explained
DMARC monitoring collects and reads receiver feedback about mail using your domain. It identifies sending sources, measures authentication alignment, and helps you decide whether a policy change will disrupt legitimate mail. Publishing a DNS record sets the requested policy; monitoring follows the results after publication.
What DMARC monitoring actually watches
The main input is the aggregate report: XML feedback sent by participating receivers to the destination in your record's rua tag. Reports commonly cover a day of observations and arrive as compressed attachments. Under RFC 9989 section 4.7, receivers must not generate aggregate reports when rua is absent.
A starting record requesting reports looks like this:
_dmarc.example.com TXT "v=DMARC1; p=none; rua=mailto:reports@example.com"
On November 4, 2026, a DNS-over-HTTPS query returned this public example with enforcement and reporting enabled together:
https://dns.google/resolve?name=_dmarc.google.com&type=TXT
v=DMARC1; p=reject; rua=mailto:mailauth-reports@google.com
The rua address requests aggregate feedback at any policy level. An external reporting destination needs authorization from the destination domain; a monitoring provider supplies the necessary instructions. Check your record with the DMARC checker before waiting for reports.
For each group of observed messages, aggregate feedback includes:
| Field | What you can investigate |
|---|---|
| Source IP | Which infrastructure sent the mail |
| Message count | The volume associated with that row |
| Applied disposition | Whether the receiver reported none, quarantine, or reject |
| DKIM result and alignment | Whether an authenticated signing domain aligned with From |
| SPF result and alignment | Whether the envelope sender authenticated and aligned with From |
| Reporting interval and receiver | When and where the observations were collected |
Aggregate reports summarize traffic rather than including message bodies or subjects. Failure reports requested through ruf are a separate format and can include detailed message information. DMARCdrift supports both aggregate and forensic reports; see what DMARCdrift receives.
Reports cover participating receivers' observations. They are not a complete delivery log or a measurement of inbox placement. Keep your sending provider's logs for individual delivery failures.
What a monitor does with raw reports
A compressed XML attachment contains nested records with counts and policy results. Reading one report with the report analyzer is useful for diagnosis. Reviewing a stream across receivers requires grouping and comparing those records.
- Parse: decompress the attachment and extract the report window, published policy, source IPs, counts, and authentication results.
- Aggregate: combine observations across receivers and reporting periods so you can compare source volumes and alignment over time.
- Surface changes: identify alignment drops, new sources, and spoofing signals. DNS polling separately detects changes to the published policy.
Keep source-level results alongside totals. A high overall alignment rate can conceal a low-volume invoicing system whose messages all fail, while a large spoofing campaign can depress the overall percentage without any change to your legitimate senders.
Setting up the record and starting monitoring
Choose a reporting destination before editing DNS. If you use DMARCdrift, follow the getting-started overview to obtain the address for your domain. Do not copy the address from another domain's record.
- Find the existing TXT record at
_dmarcfor your sending domain. Edit that policy rather than creating a competing second record. - Add the supplied
ruadestination. Keep the existing policy unless you have separately reviewed an enforcement change. - If starting without a policy, publish
p=nonewhile you inventory senders and investigate alignment. - Resolve the record after publication and check the reporting destination and syntax. Complete external destination authorization where required.
- Wait through a reporting cycle, then inspect the receiver and reporting-window fields in the first arrivals. No immediate report does not mean your DNS change failed.
See the DMARC record reference for tag syntax. Continue monitoring after enforcement: changing DNS providers, replacing an email service, or adding a support platform can alter the configuration later.
What monitoring surfaces
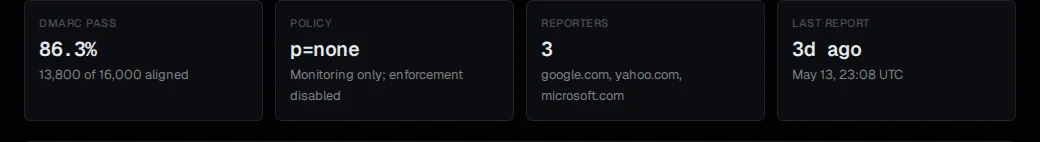
Alignment rate is the share of reported messages for which SPF or DKIM passed in alignment with the visible From domain. Use message counts, rather than counting report rows equally. The alignment-rate documentation explains the dashboard calculation. Review failures by legitimate source before judging readiness from the total.
Sending sources identify IPs and, where recognizable, the services behind them. Compare those sources with your transactional, marketing, invoicing, and support providers. Treat an unfamiliar label as an investigation task: forwarding, shared infrastructure, or a forgotten integration can explain it.
Spoofing signals combine authentication failures, source information, and volume. Repeated unaligned traffic from an unauthorized source warrants investigation. Aggregate feedback does not identify the person behind it.
Policy and DNS drift capture changes to the published record. Losing rua during a DNS migration stops the requested feedback; changing p=reject to p=none changes your handling preference. Compare a detected change with the intended DNS edit and the record currently resolving.
How monitoring supports none, quarantine, and reject
DMARCdrift's November 1, 2026 adoption scan found 151 of 2,241 selected domains at p=none. Another 1,580 were classified at full p=reject. That curated DNS snapshot describes published policies, not how often their owners review reports.
At p=none, you request no DMARC-specific enforcement. Receivers continue their own spam filtering. Use reports to inventory legitimate senders, check aligned authentication, and distinguish configuration failures from unauthorized traffic.
At p=quarantine, you ask receivers to treat failing mail as suspicious. Watch known senders' results and their delivery logs after the change. Confirm that low-volume flows such as billing notices and password resets still work.
At p=reject, you express the strongest handling preference for failures. Keep reviewing new sources and regressions. Receivers make the final delivery decision using DMARC and their other signals; RFC 9989 explicitly discusses forwarding and mailing-list interoperability.
There is no universal alignment percentage that makes an enforcement change safe. Account for every legitimate sending stream and its normal schedule, including infrequent campaigns. The enforcement readiness checklist and roadmap provide the rollout steps.
The revised specification retires pct, so percentage sampling is not a dependable safety mechanism across old and new receivers. Review the pct migration guide, including testing mode, before changing a partially enforced record.
SPF and DKIM failures behind the reports
SPF checks whether the connecting IP is authorized for the envelope sender domain. The 10-lookup limit includes nested DNS-querying mechanisms and modifiers. Exceeding it produces permerror; remove obsolete includes or review the SPF flattening guide before adding more services. Editing your website's root SPF does not repair a provider that uses a different envelope domain.
DKIM verifies a signature associated with the d= signing domain. DMARC then checks that domain's alignment with From. A valid signature from a provider's unrelated domain is insufficient for DKIM alignment. Configure domain signing at each provider and verify delivered test messages. Forwarding commonly breaks SPF; intact DKIM signatures can preserve an aligned pass through that forwarding path.
DMARC needs either mechanism to pass and align, while bulk-sender programs can require both SPF and DKIM configuration. See DKIM versus DMARC for their different roles.
A practical report review checklist
- Check the receiver and reporting interval so you compare equivalent periods rather than partial days.
- Match known sources to your provider inventory. Inspect SPF and DKIM alignment separately when a source fails.
- Investigate unfamiliar sources using volume, authentication results, and your integration history before classifying them as abuse.
- Compare failures over time and with recent DNS, provider, or campaign changes.
- Use the findings to repair legitimate senders and decide whether to change policy. Continue reviewing after each change.
Monitoring is especially useful when you have multiple sending providers, are preparing for enforcement, or need to spot policy drift. For a single-file investigation, start with the report analyzer; for a DNS diagnosis, use the email authentication checker.